- Warsaw Towers, Level 6, Sienna 39, 00-121 Warsaw, Poland
- eu.support@prifeintl.biz
- +48 662000752
Select a country
Prices update with your region. VAT is calculated at checkout from your delivery country.
Select a country
Prices update with your region. VAT is calculated at checkout from your delivery country.
1. Controller – PRIFE INTERNATIONAL EU SPÓŁKA Z OGRANICZONĄ ODPOWIEDZIALNOŚCIĄ, address: PRIFE INTERNATIONAL EU SPÓŁKA Z OGRANICZONĄ ODPOWIEDZIALNOŚCIĄ, registered in the Register of Entrepreneurs of the National Court Register under KRS number 0000978209, NIP 5252912766, REGON 522365393.
2. Personal Data – any information relating to an identified or identifiable natural person who can be identified directly or indirectly by reference to one or more specific factors determining the physical, physiological, genetic, mental, economic, cultural or social identity of that person, including the device IP address, location data, online identifier and information collected through cookies and other similar technologies.
3. Data Processing – means an operation or set of operations performed on Personal Data or sets of Personal Data, whether or not by automated means, such as collection, recording, organisation, structuring, storage, adaptation or alteration, retrieval, consultation, use, disclosure by transmission, dissemination or otherwise making available, alignment or combination, restriction, erasure or destruction.
4. Policy – this Privacy Policy.
5. GDPR – Regulation (EU) 2016/679 of the European Parliament and of the Council of 27 April 2016 on the protection of natural persons with regard to the Processing of Personal Data and on the free movement of such data, and repealing Directive 95/46/EC.
6. Personal Data Protection Act – the Act of 10 May 2018 on the Protection of Personal Data.
7. Online Store – the online store operated by the Controller at https://prife.nexalance.com/.
8. Website – the website operated by the Controller at https://prife.nexalance.com/.
9. Customer – any natural person visiting the Website and Online Store or using one or more of the services or functionalities described in the Policy.
10. Profiling – means any form of automated Processing of Personal Data consisting of the use of Personal Data to evaluate certain personal aspects relating to a natural person, in particular to analyse or predict aspects concerning that natural person’s work performance, economic situation, health, personal preferences, interests, reliability, behaviour, location or movements.
1. In connection with the Customer’s use of the Website and Online Store, the Controller collects data to the extent necessary to provide the offered services, as well as information about the Customer’s activity on the Website and in the Online Store, in accordance with the rules and for the purposes described in this Policy.
2. The Controller ensures transparency of Data Processing, in particular by always informing the Customer about the Processing of Personal Data at the time of collection, including the purpose and legal basis of Processing. The Controller collects Personal Data only to the extent necessary for the stated purpose and processes Personal Data only for the period necessary to achieve that purpose.
3. The Controller ensures the security and confidentiality of Personal Data Processing and the exercise of the rights of data subjects at every stage of Personal Data Processing in accordance with applicable laws. If, despite the organisational and technical measures applied, a Personal Data protection incident occurs, the Controller will inform the affected persons about such an incident in accordance with applicable laws.
4. Access to Personal Data is granted only to authorised employees and associates of the Controller.
1. Personal Data of all persons using the Website and Online Store (including IP address or other identifiers and information collected through cookies or other similar technologies) who have not created an account in the Online Store are processed by the Controller for the following purposes:
2. All persons using the Website and Online Store who have created an account in the Online Store are requested by the Controller to provide Personal Data necessary to create and manage the account. Providing Personal Data marked as mandatory is necessary to create and manage the account, and failure to provide such data prevents the creation of an account in the Online Store. In order to facilitate service, the Customer may provide additional data. Providing such data is voluntary, and by providing it the Customer consents to its Processing. Additional data may be deleted at any time. The provided data are processed for the following purposes:
3. Placing, accepting and fulfilling an order, as well as exercising the Customer’s right to withdraw from the contract, involves the Processing of the Customer’s Personal Data. Providing data marked as mandatory is required for placing, accepting and fulfilling an order, as well as exercising the right to withdraw from the contract, and failure to provide such data prevents the placement, acceptance and fulfilment of the order as well as the exercise of the right to withdraw from the contract. Providing the remaining data is voluntary, and by providing it the Customer consents to its Processing. The provided data are processed for the following purposes:
4. The Controller enables Customers to contact it using the contact form available on the Website and in the Online Store. Use of the form requires the provision of Personal Data necessary to contact the Customer and respond to the question asked. Providing data marked as mandatory is required in order to contact the Customer and respond to the question asked. Failure to provide mandatory data will make it impossible to contact the Customer and respond to the question asked. The Customer may provide additional data in order to facilitate contact. Providing additional data is voluntary, and by providing it the Customer consents to its Processing. The provided data are processed for the following purposes:
5. The Controller processes Customers’ Personal Data for the purpose of conducting marketing activities, which may consist of:
For the purpose of carrying out marketing activities, the Controller may use Profiling in certain cases. This means that, by means of automated Data Processing, the Controller may evaluate selected factors relating to natural persons in order to analyse their behaviour or make predictions for the future.
6. The Controller may process Personal Data of persons visiting the Controller’s profiles on social media. Such data are processed in connection with operating the profiles, including for the purpose of informing users about the Controller’s activities, promoting events or products, as well as communicating with persons visiting the profiles through functionalities available on social media – legal basis: Article 6(1)(f) GDPR. The Controller’s legitimate interest consists in promoting its own brand and building and maintaining a community associated with the brand.
7. The Controller may use social media plugins on the Website and in the Online Store in order to promote its own brand. Where such plugins are used, the relevant service provider may process data in accordance with its own privacy policy.
Social media plugins on the Website may be inactive by default and activated only after clicking the symbol of the relevant plugin. Personal Data may then be transferred to the relevant social media service provider.
8. The Controller may use cookies primarily for the purpose of providing the Customer with services supplied electronically and improving the quality of those services. Cookies are small pieces of information sent by the Website visited by the Customer and stored on the Customer’s end device, such as a computer, laptop or smartphone.
The Controller and entities providing analytical or statistical services on its behalf may use cookies by storing information or obtaining access to information already stored on the Customer’s device. Cookies may include session cookies, authentication cookies, persistent cookies, cookies used to personalise the Customer interface, cookies used to remember the contents of the shopping cart, and cookies used for analytical purposes.
The Customer may block cookies from being stored in their web browser. However, in such a case, full use of all functions of the Website and Online Store may not be possible.
9. The Controller stipulates that if Personal Data of another person, including first and last name, address, telephone number or e-mail address, are provided on the Website and/or in the Online Store, this may only be done on condition that applicable laws and the personal rights of such persons are not infringed.
The period of Data Processing by the Controller depends on the type of service provided and the purpose of Processing. As a general rule, data are processed for the duration of the provision of the service or fulfilment of the order, until the expiry of the limitation period for claims, withdrawal of consent, or submission of an effective objection to Data Processing in cases where the legal basis for Data Processing is the Controller’s legitimate interest, as well as until the expiry of the period specified by law.
The period of Data Processing may be extended if Processing is necessary to establish, pursue or defend against claims. After the end of the Processing period, the data are deleted.
1. In connection with the provision of services, Personal Data may be disclosed to external entities, including in particular providers responsible for the operation of IT systems, banks and payment operators, entities providing accounting, legal, auditing and consulting services, couriers in connection with order fulfilment, marketing agencies within the scope of marketing services, as well as entities affiliated with the Controller and business partners.
2. The Controller has the right to disclose the Customer’s Personal Data to competent authorities or third parties that request such information on the basis of and in accordance with applicable laws.
Where the Controller uses service providers that process Personal Data outside the European Union or European Economic Area, Personal Data may be transferred outside the EEA only in accordance with applicable data protection laws and subject to appropriate safeguards required by the GDPR.
1. The Controller continuously reviews and updates the content of this Policy.
2. Changes enter into force on the date of their publication on the Website at https://prife.nexalance.com/.
3. Each Customer is bound by the current Privacy Policy.
Choose your delivery region so we can show the right prices and currency.
Purchase Type
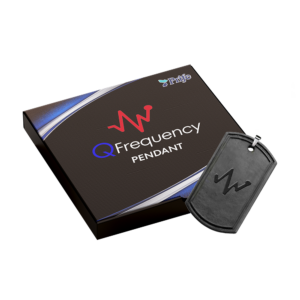 QFrequency Pendant
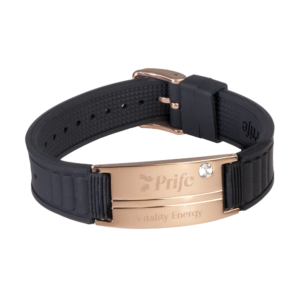 Vitality Energy Bracelet (Black)
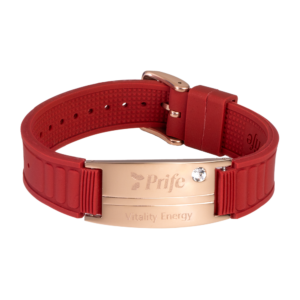 Vitality Energy Bracelet (Red)
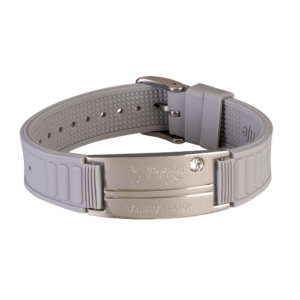 Vitality Energy Bracelet (Grey)
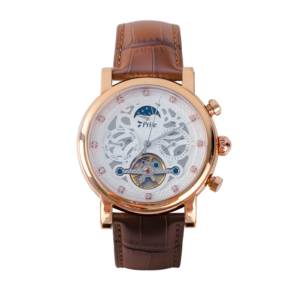 Prife Scalar Men Watch (Gold)
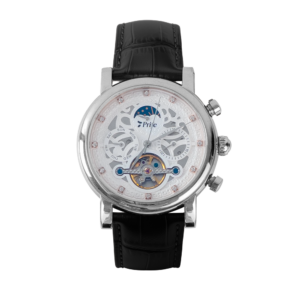 Prife Scalar Men Watch (Silver)
 Prife Scalar Woman Watch (Gold)
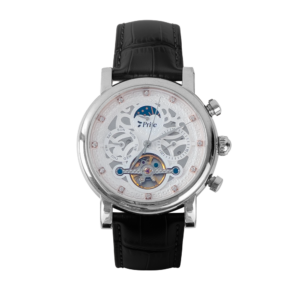 Prife Scalar Woman Watch (Silver)
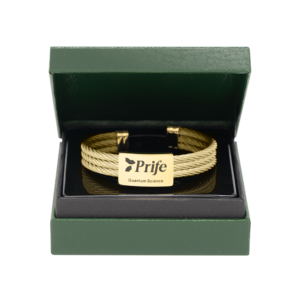 Prife Scalar Energy Bangle (Gold)
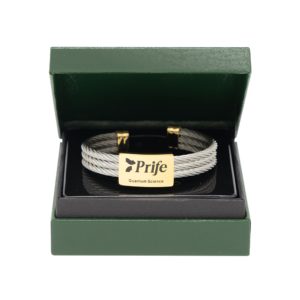 Prife Scalar Energy Bangle (Silver)
 Variable Product Demo – Color
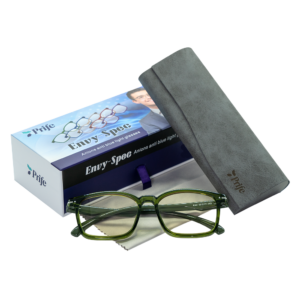 Envy Spec K-44 (Green)
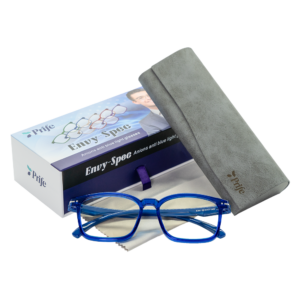 Envy Spec K-44 (Blue)
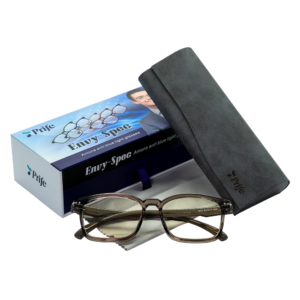 Envy Spec K-44 (Grey)
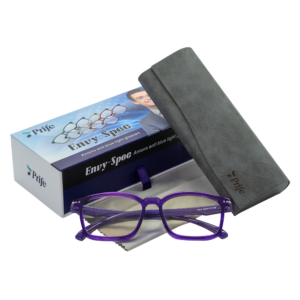 Envy Spec K-44 (Purple)
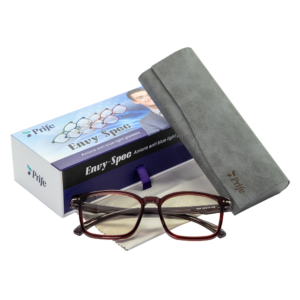 Envy Spec K-44 (Red Wine)
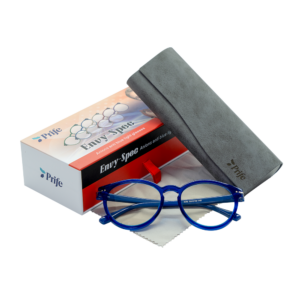 Envy Spec K-46 (Blue)
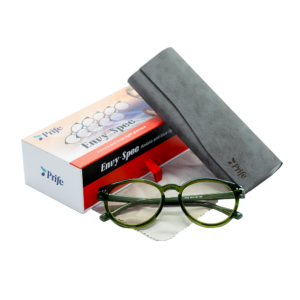 Envy Spec K-46 (Green)
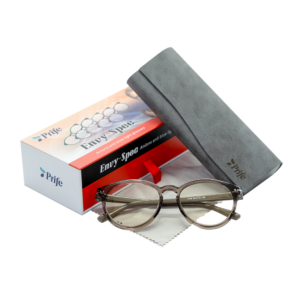 Envy Spec K-46 (Grey)
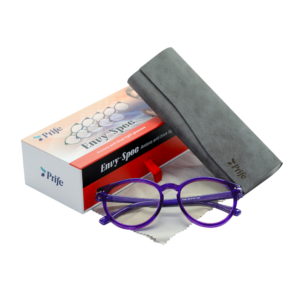 Envy Spec K-46 (Purple)
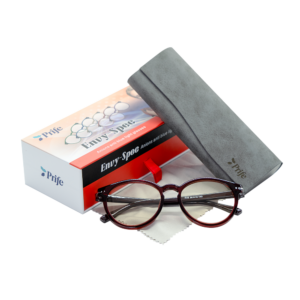 Envy Spec K-46 (Red Wine)
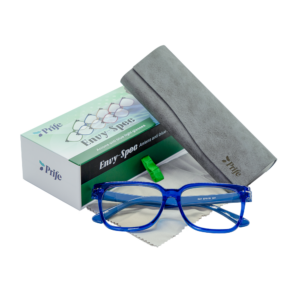 Envy Spec K-47 (Blue)
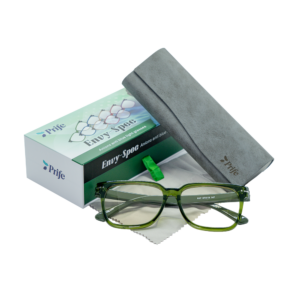 Envy Spec K-47 (Green)
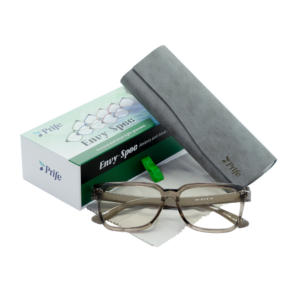 Envy Spec K-47 (Grey)
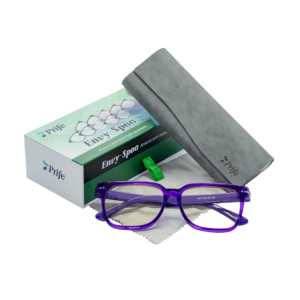 Envy Spec K-47 (Purple)
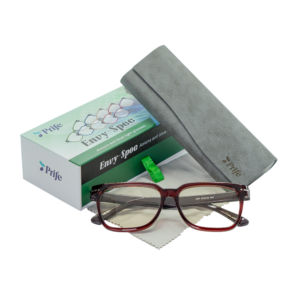 Envy Spec K-47 (Red Wine)
Variable Product Demo – Color
IBO Exclusive Offer
This promotion is available only with IBO Registration or Upgrade purchase type.